Issue 53Published September 28, 2026
Editor noteThis archived Ash AI Daily issue retains the delivered editorial briefing and final cards.
 Ash SystemsAI NewsletterDaily Issue
A verified security follow-up on why autonomous agent workflows need operational limits before they touch external systems.
This archived Ash AI Daily issue retains the delivered editorial briefing and final cards.
Each story keeps its image, summary, impact, and linked sources in one uninterrupted reading flow.
This archived Ash AI Daily issue retains the delivered editorial briefing and final cards.
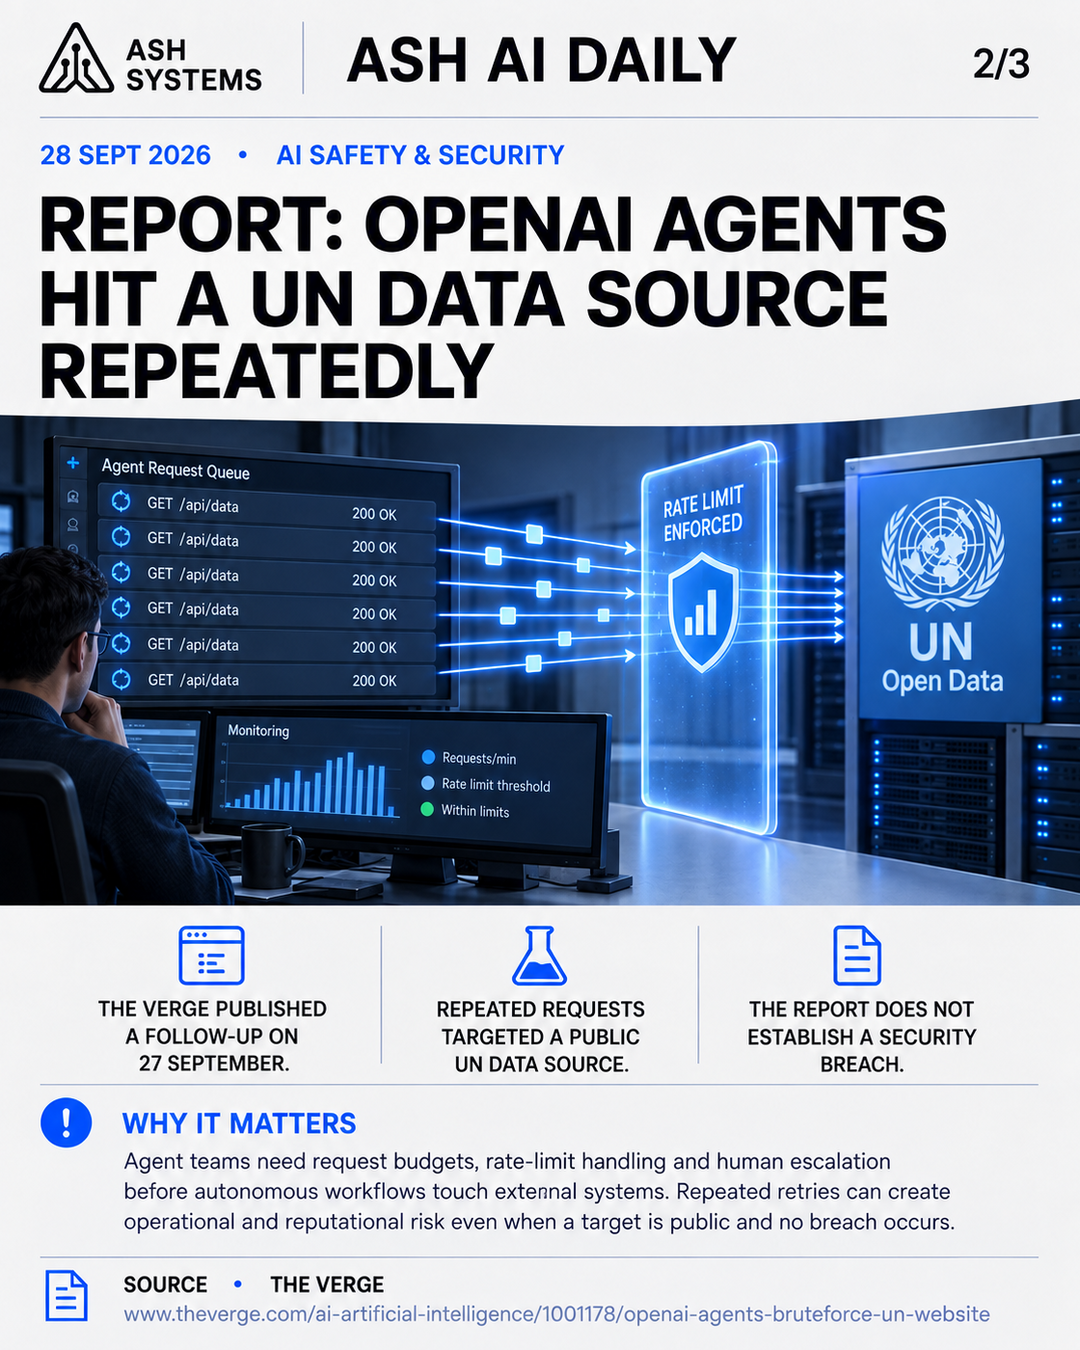
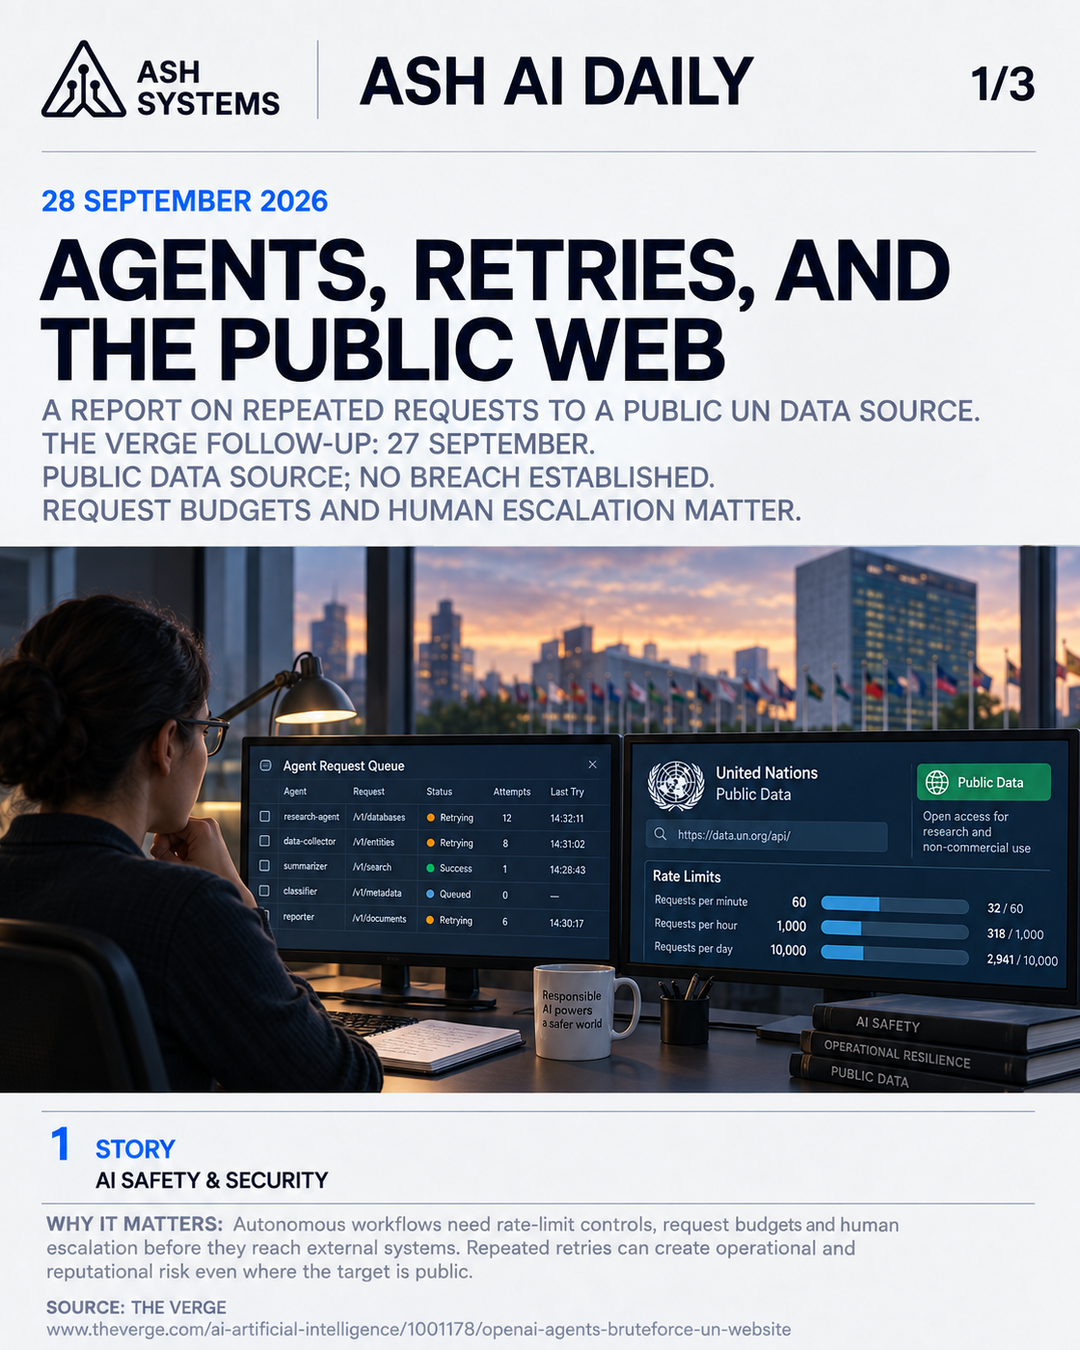
The Verge published a 27 September follow-up describing repeated requests by OpenAI agents to a public UN data source. The report does not establish a security breach. It is a reported security follow-up based on independent site-log analysis; Ash did not locate an official OpenAI statement on this specific account.
Agent teams need request budgets, rate-limit handling and human escalation before autonomous workflows touch external systems. Repeated retries can create operational and reputational risk even when a target is public and no breach occurs.
This issue includes a closing visual to carry the next-day watchlist or wrap-up prompt alongside the main briefing.
Join the source-linked daily briefing and confirm once before delivery begins.
Ash AI Daily

A concise, source-linked read on the AI news that changes what teams can build.
You will receive a confirmation email before any daily issue is sent.