Issue 60Published October 5, 2026
Editor noteThis archived Ash AI Daily issue retains the delivered editorial briefing and final cards.
 Ash SystemsAI NewsletterDaily Issue
Google’s pause of an open-source vulnerability rewards program is a practical warning: security teams need safeguards that preserve the value of AI-assisted research without letting invalid reports consume the review queue.
This archived Ash AI Daily issue retains the delivered editorial briefing and final cards.
Each story keeps its image, summary, impact, and linked sources in one uninterrupted reading flow.
This archived Ash AI Daily issue retains the delivered editorial briefing and final cards.
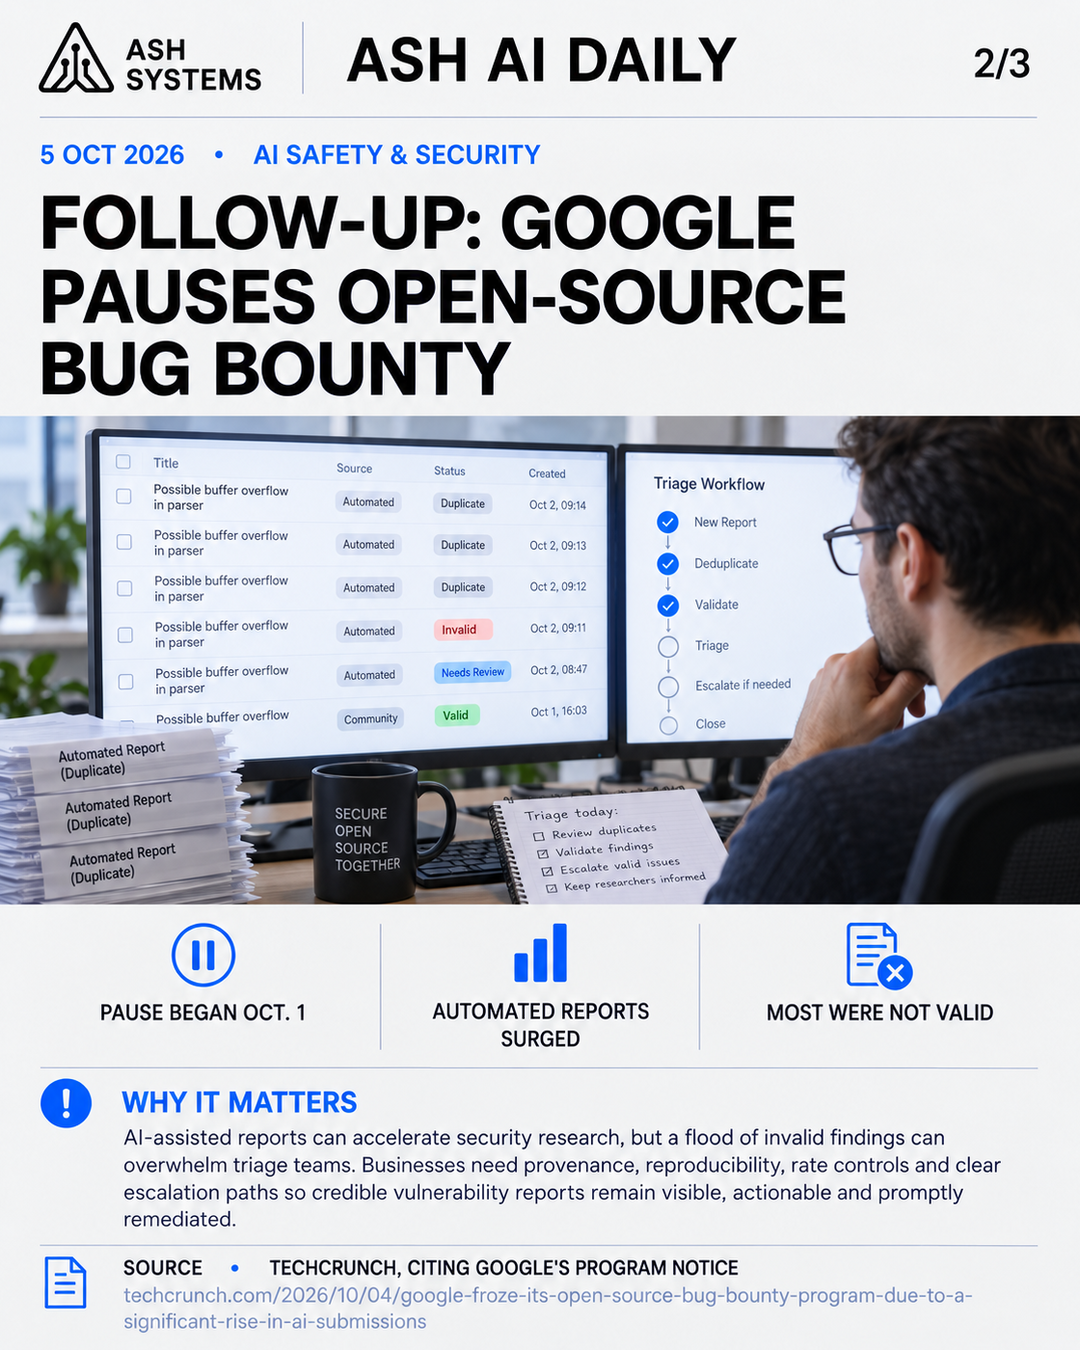
Google paused its Open Source Software Vulnerability Rewards Program on October 1, according to its published program notice. TechCrunch reported on October 4 that Google cited a significant rise in automated submissions and said most were not valid. This is a follow-up: the underlying program change began before this issue’s window, while the detailed report was published during it.
AI can help researchers find issues, but automated low-quality reports can turn a bug bounty into a triage bottleneck. Teams operating vulnerability intake need reproducibility checks, rate controls, provenance signals and escalation paths that preserve capacity for credible findings.
This issue includes a closing visual to carry the next-day watchlist or wrap-up prompt alongside the main briefing.
Join the source-linked daily briefing and confirm once before delivery begins.
Ash AI Daily

A concise, source-linked read on the AI news that changes what teams can build.
You will receive a confirmation email before any daily issue is sent.